Reveelium UEBA
Intelligent SIEM UEBA, Threat Hunting, XDR, and SOAR
Maximize your cybersecurity with artificial intelligence
Reveelium is a SIEM UEBA behavioral analysis technology that enables the detection of known and unknown cyber threats: APTs (Advanced Persistent Threats), unknown malware, viruses, data leaks, data theft, and abnormal behavior within information systems, while tracing the footprints of cyberattacks. Combining AI, Threat Hunting, Threat Intelligence, and SOAR (« Security Orchestration, Automation, and Response »), Reveelium allows you to capitalize on events that may threaten the information system and anticipate threats.
THE AVERAGE DETECTION TIME FOR MALWARE IS 16 MONTHS!
Key strengths
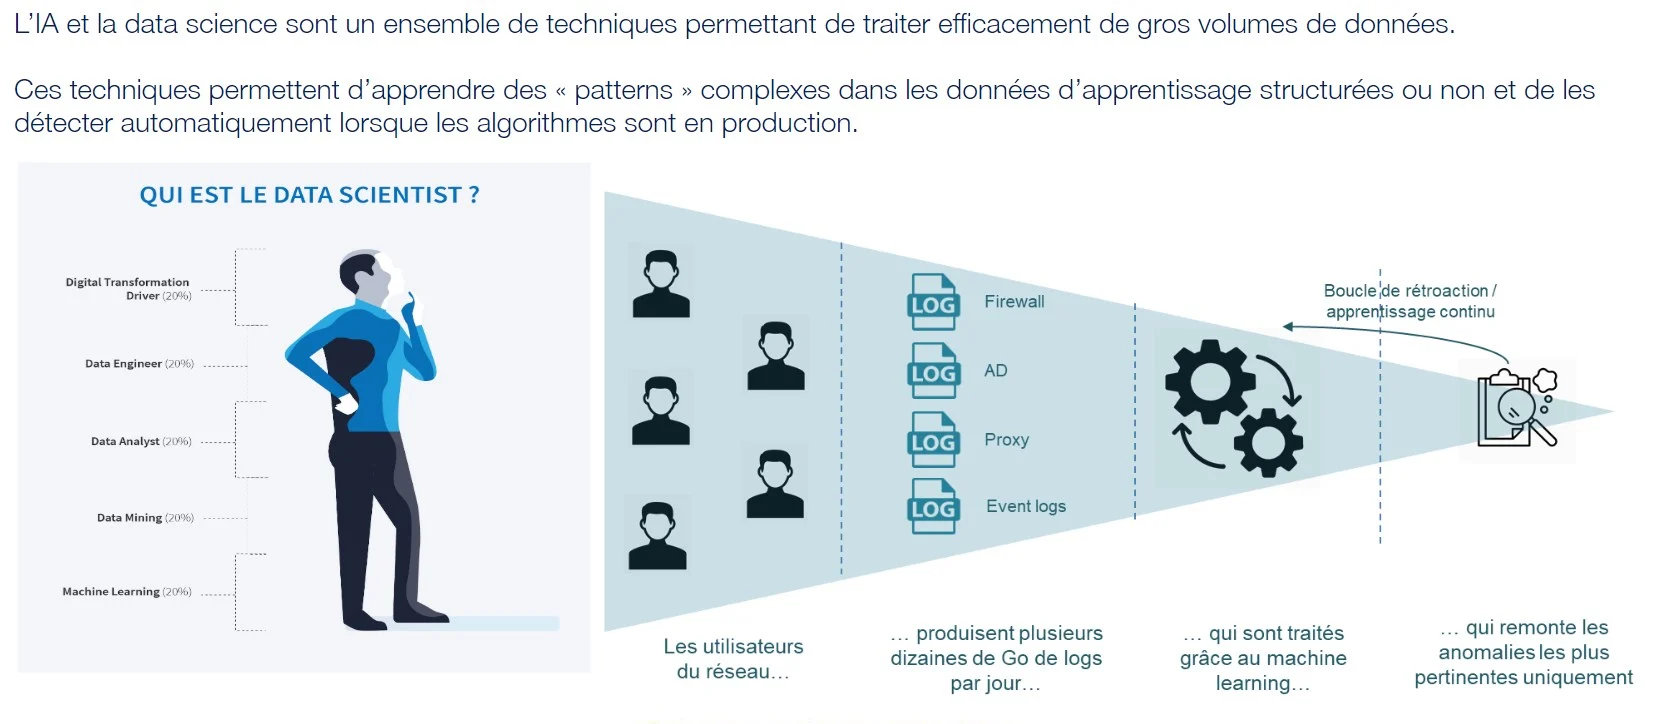
Reveelium is a next-generation security tool whose richness and strength lie in the use of 3 complementary engines.
All 3 engines operate on a big data platform capable of processing large volumes of data and logs from IT or OT sensors.
Business rules are implemented and tracked in the business correlator. The GUI displays correlations and tracks deviations, enabling user interaction and feedback.
Reveelium technology is unique in Europe.
Benefits of the solution
Advanced Threat Detection
Reveelium allows you to detect deviant or malicious behavior within information systems thanks to Artificial Intelligence algorithms that amplify your log analysis tenfold with machine learning and intelligent correlation. Only Artificial Intelligence enables real-time analysis of massive volumes of data to identify
current or emerging threats.
Detecting attacks with UEBA
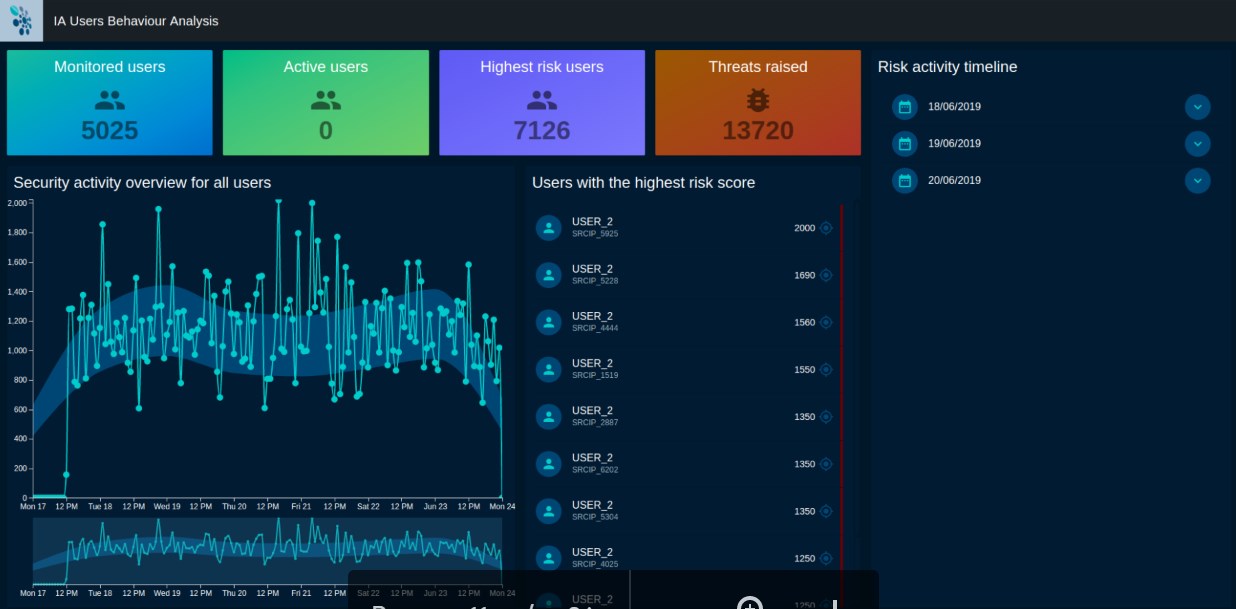
Reveelium detects abnormal machine and user behavior thanks to its UEBA (User and Entity Behavior Analytics) technology: immediately upon installation, unsupervised learning algorithms identify the behavior of all assets on the system and pinpoint relevant, contextualized anomalies.
The approach combines machine learning and deep learning methods from academic cybersecurity research: graph theory, LSTM-type recurrent neural networks, supervised and unsupervised classification algorithms, and more.
Reduction of false positives
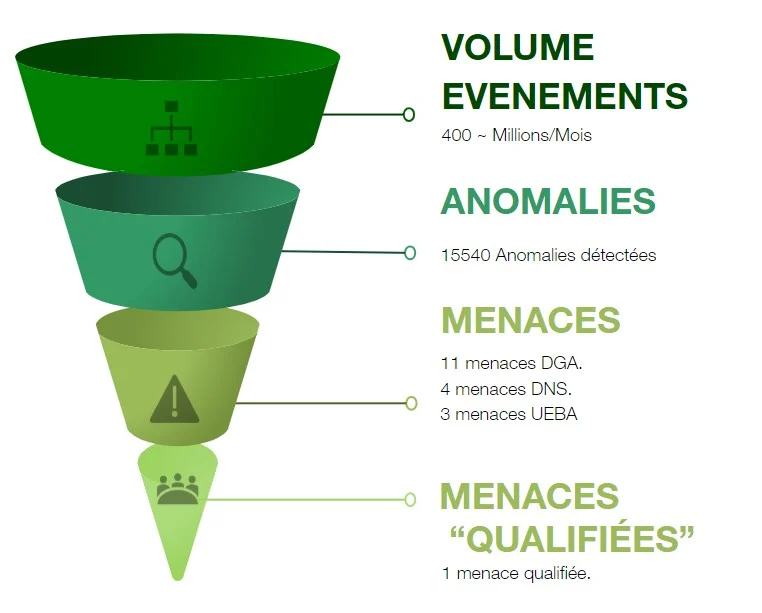
Reveelium reduces the number of false positives across the information system. Reveelium synthesizes the threats resulting from
the set of alerts identified as constituting the threat. This innovative method allows teams to focus exclusively on the verified threat without wasting time analyzing hundreds of irrelevant alerts.
Reveelium and Forensic Mode
Reveelium technology enables offline log analysis to conduct digital forensics operations or post-incident audits of information system activities. In this "cold log review" configuration, logs can be ingested into a Reveelium lab environment to verify that conventional controls have not missed a cyber threat or deviant behavior indicative of a cyberattack or insider fraud.
360° threat visibility
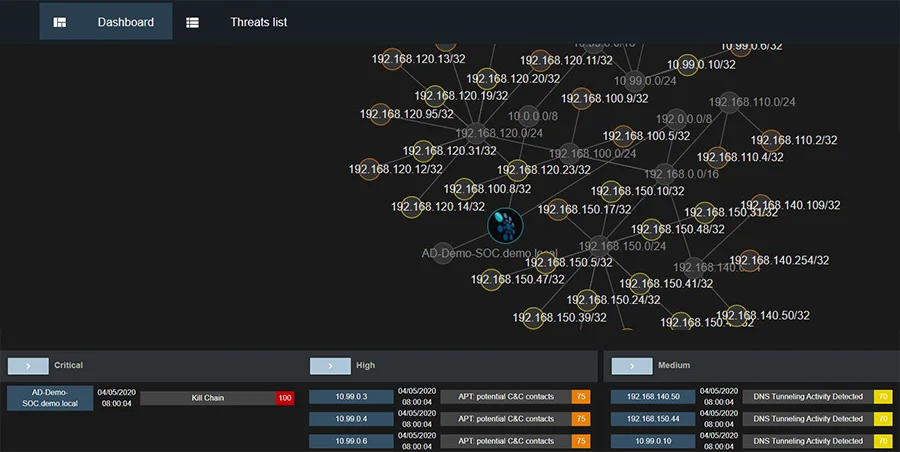
Reveelium delivers a comprehensive view of all impacted assets across your network.
Our solution maps the entire network at risk of lateral movement, identifies the associated IP addresses, and helps prevent threat propagation.
Identification of abnormal behavior via decision tree
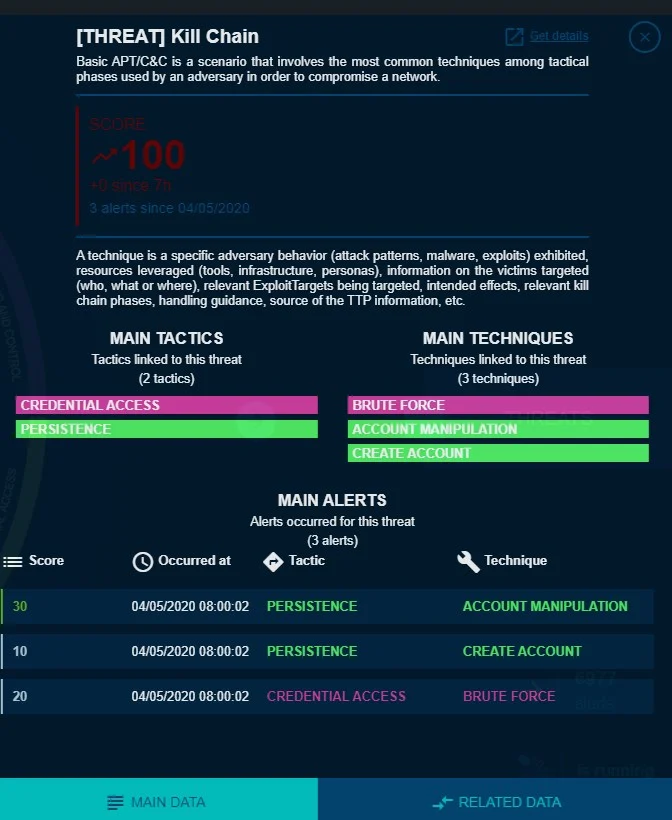
Reveelium identifies the origin and path of behavior considered abnormal within the IS, presenting its characteristics. It is capable of identifying alerts that constitute a threat and displaying the decision logic that led to escalating the severity rating of that threat.
Once the threat is proven and recognized, the technology identifies similar behaviors within the information system and can outline potential attack scenarios to protect against them.
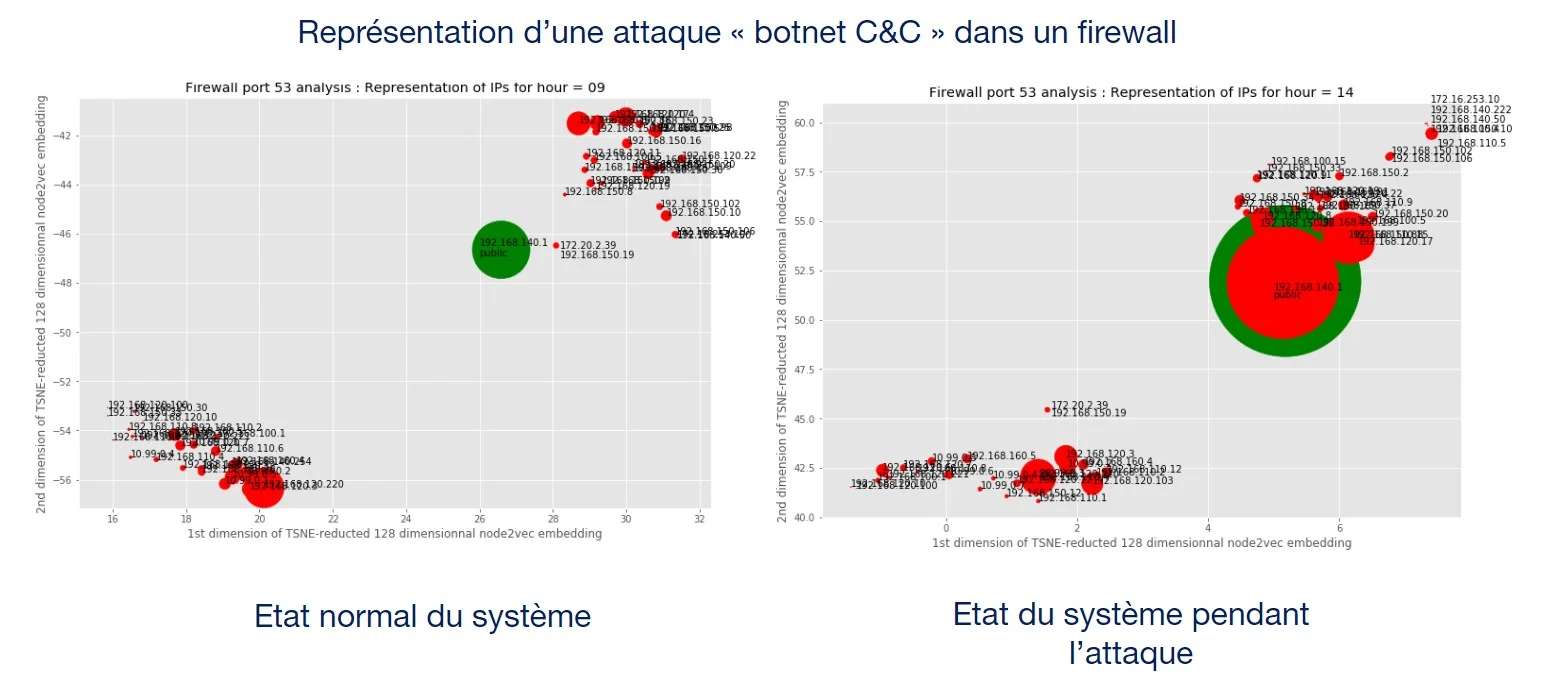
Custom use cases on demand
In addition to tuning our algorithms with cybersecurity-dedicated metadata and use cases, we offer our clients the development of custom use cases to deploy Reveelium within specific operational contexts.
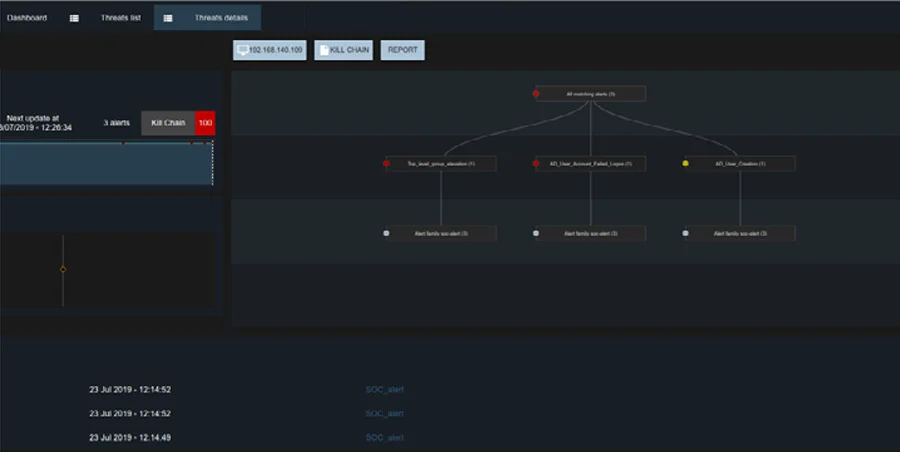
Threat measurement powered by artificial intelligence
Reveelium automatically generates reports to quantify its activity and includes threat-related indicators: affected IP(s), alert counts per threat, criticality indices, histograms, threat risk evolution over time, decision trees, and more.
Rapid identification of current threats
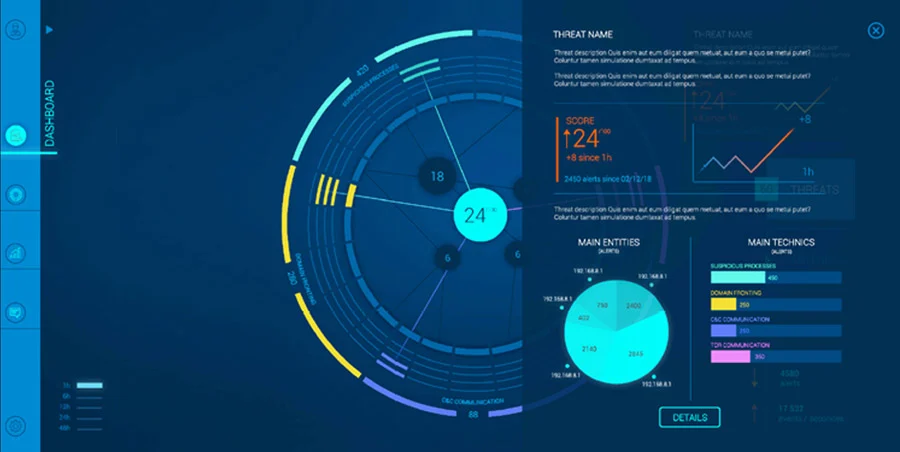
Reveelium’s graphical interface dynamically maps the tactical and technical dimensions
of cyberattacks, quickly identifying the typology of potential or active attacks to enable immediate response.
Reveelium UEBA integrates the MITRE ATT&CK matrix to pinpoint the tactics and techniques used by the identified threat before it propagates.
Our value proposition
What our clients say
« We hadn’t identified any products on the market that could protect us against advanced cyber threats. Until we discovered Reveelium. We have been using it for several years and it allows us to move from a reactive model to a preventive model. We haven’t had a single incident for several years with this technology… »
 A. Godde, CIO, Nutrition & Santé
Our clients
Accreditations and certifications