Reveelium SIEM
Security Information and Event Management
Ever-increasing risks and losses
3 out of 4 companies are subject to cyberattacks or hacking (source: Verizon).
However, 90% are equipped with baseline security tools that fail to detect these malicious attacks. APTs, malicious behavior, viruses, and ransomware bypass existing security defenses, and no conventional tool can detect these threats. Yet, these attacks leave identifiable forensic footprints.
Uncovering these malicious traces across massive volumes of data and operationalizing these signals is impossible with legacy tools.
Reveelium correlates and aggregates all types of logs from an information system, detecting active attacks and ongoing malicious activity.
An essential tool in combating advanced cyber threats, Reveelium SIEM can be deployed standalone or augmented by Ikare, Reveelium UEBA, or ITrust’s Acsia EDR to deliver a true next-generation Security Operations Center (SOC).
8 OUT OF 10 TIMES, A COMPROMISED COMPANY DOES NOT KNOW IT HAS BEEN BREACHED!
Objectives
Our Strengths
Understanding and analyzing observable telemetry across an information system is essential to ensuring its security.
A SIEM has become a foundational building block for any enterprise, crucial for establishing defense-in-depth against emerging threats. Here are our core principles:
A flexible, intuitive solution that enables us to deliver a high-performance SIEM solution at an optimized cost.
Advanced Features
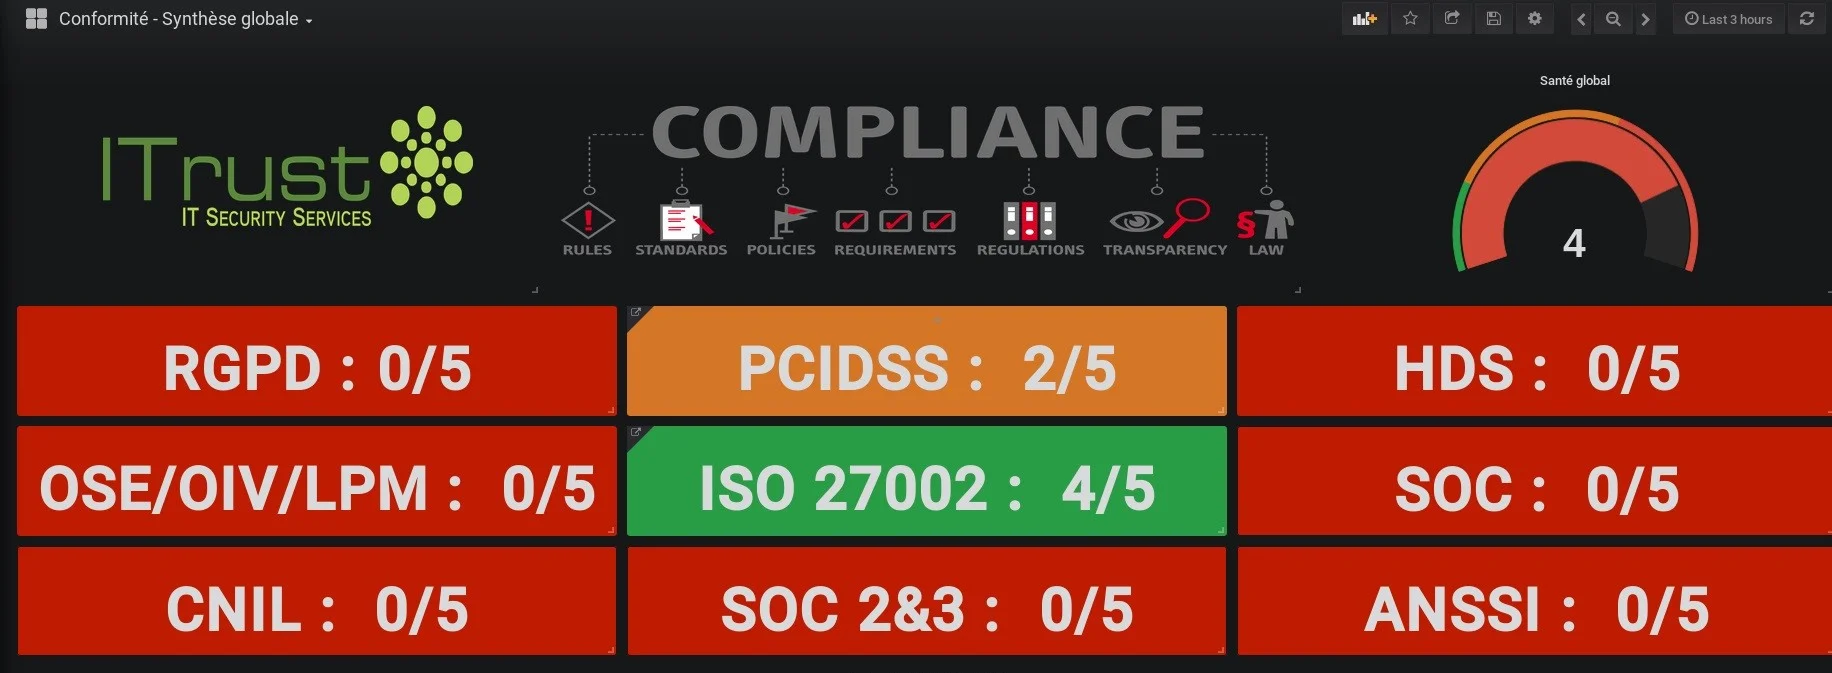
Regulatory Compliance
This core component centralizes and securely archives logs from datacenter infrastructure, delivering metrics and executive dashboards aligned with the organization's information security policy.
At a glance, Reveelium enables you to manage your entire cybersecurity policy for a variety of profiles: experts, managers, compliance officers, DPOs, CISOs, and directors. Reveelium provides a dozen out-of-the-box dashboards and allows you to build custom indicators tailored to your ISSP.
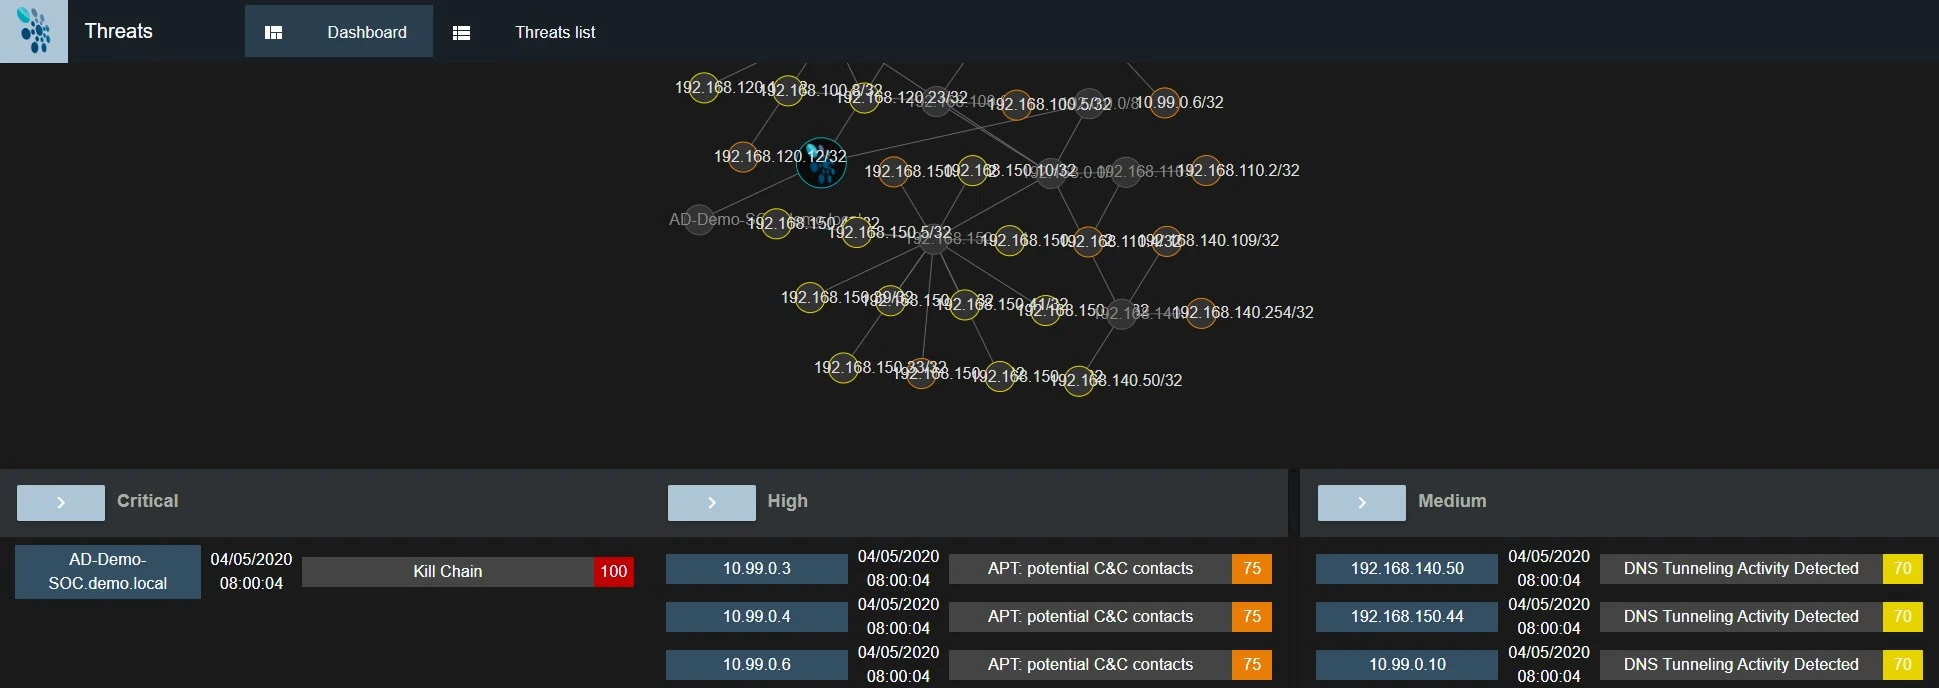
Investigation, Analysis
SIEM allows you to centralize your infrastructure, cloud, and internal application logs. You can categorize your logs using tags and leverage the robust search capabilities of Reveelium and Elastic to uncover precise contextual information about your infrastructure. You can also configure alerts to be automatically notified when critical events occur in your system.
When it comes to troubleshooting, knowing where to start can be challenging. Reveelium SIEM automatically visualizes the primary trends emerging across your data. Simply click to drill down and up through datasets, helping you identify trends and anomalies related to an incident and pinpoint its root cause.
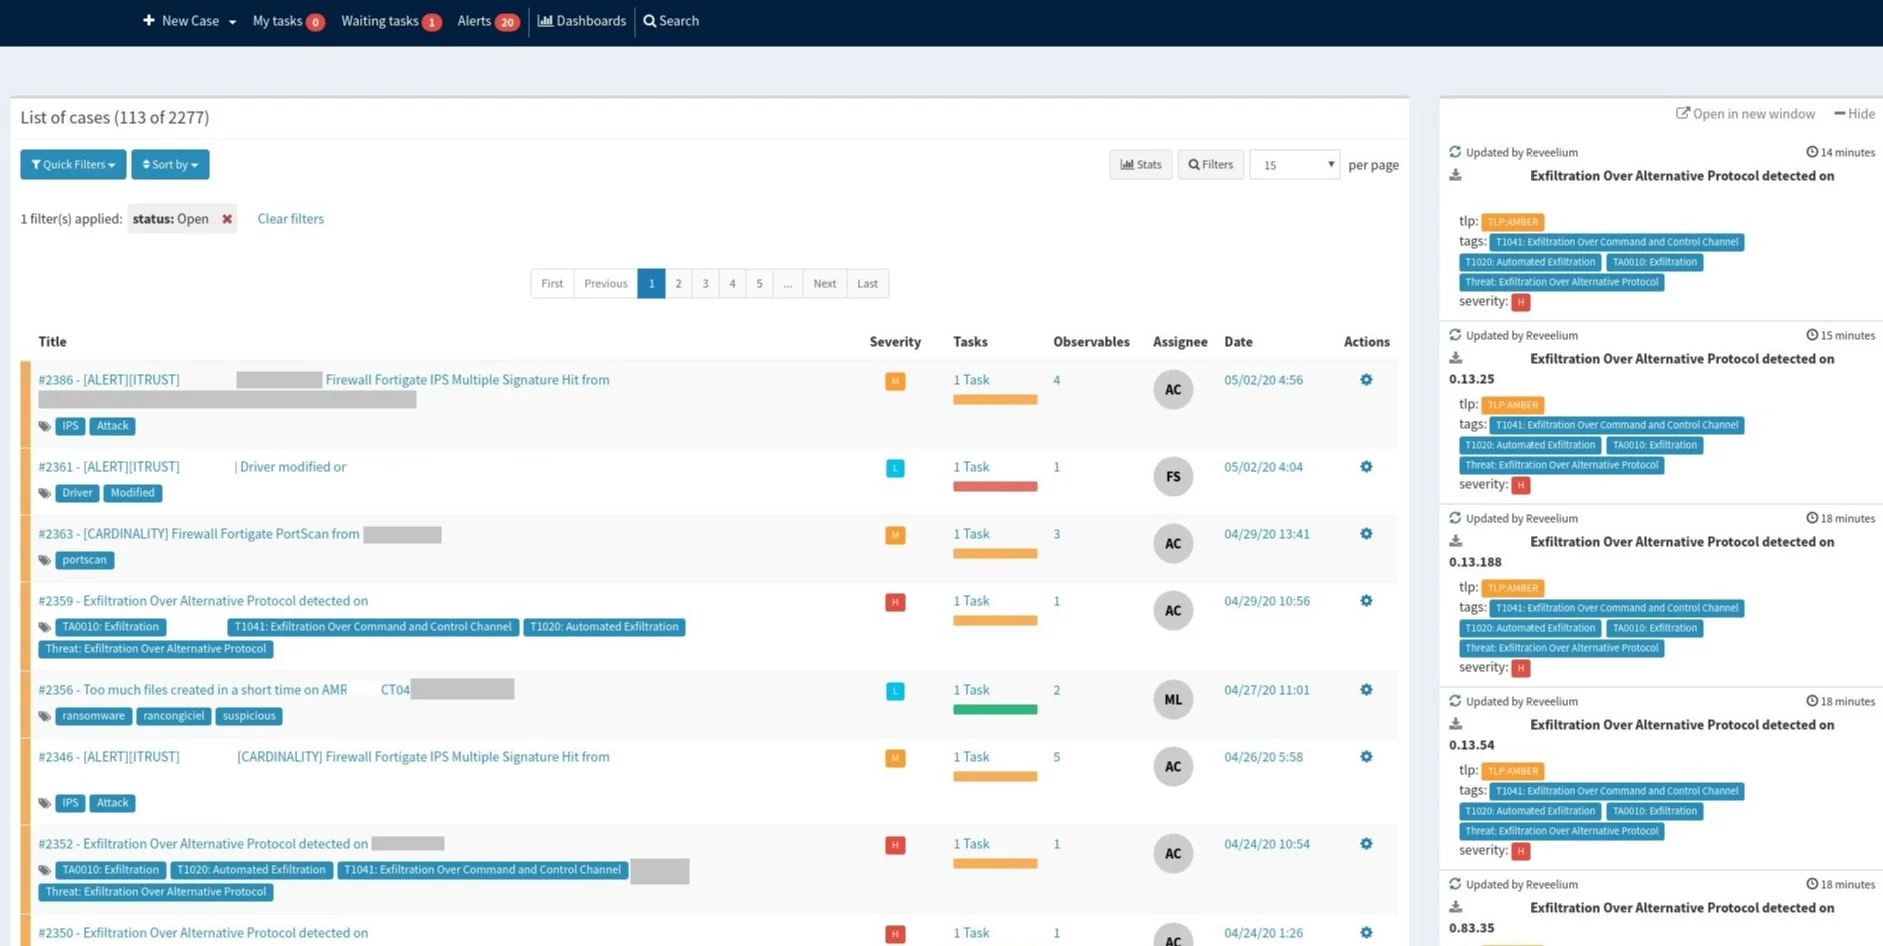
Detection, Correlation, Alerting
You can use the Alerts feature to receive automatic notifications for critical events occurring in your environment.
Reveelium allows you to create various types of alerts and "boxes".
More than 600 Sigma, detection, and correlation rules are integrated by default into Reveelium.
When setting up alerts, Reveelium guides you step-by-step through an alert wizard. At any time, you can switch to another alert or consult in-depth alert details on the Alert Overview page.
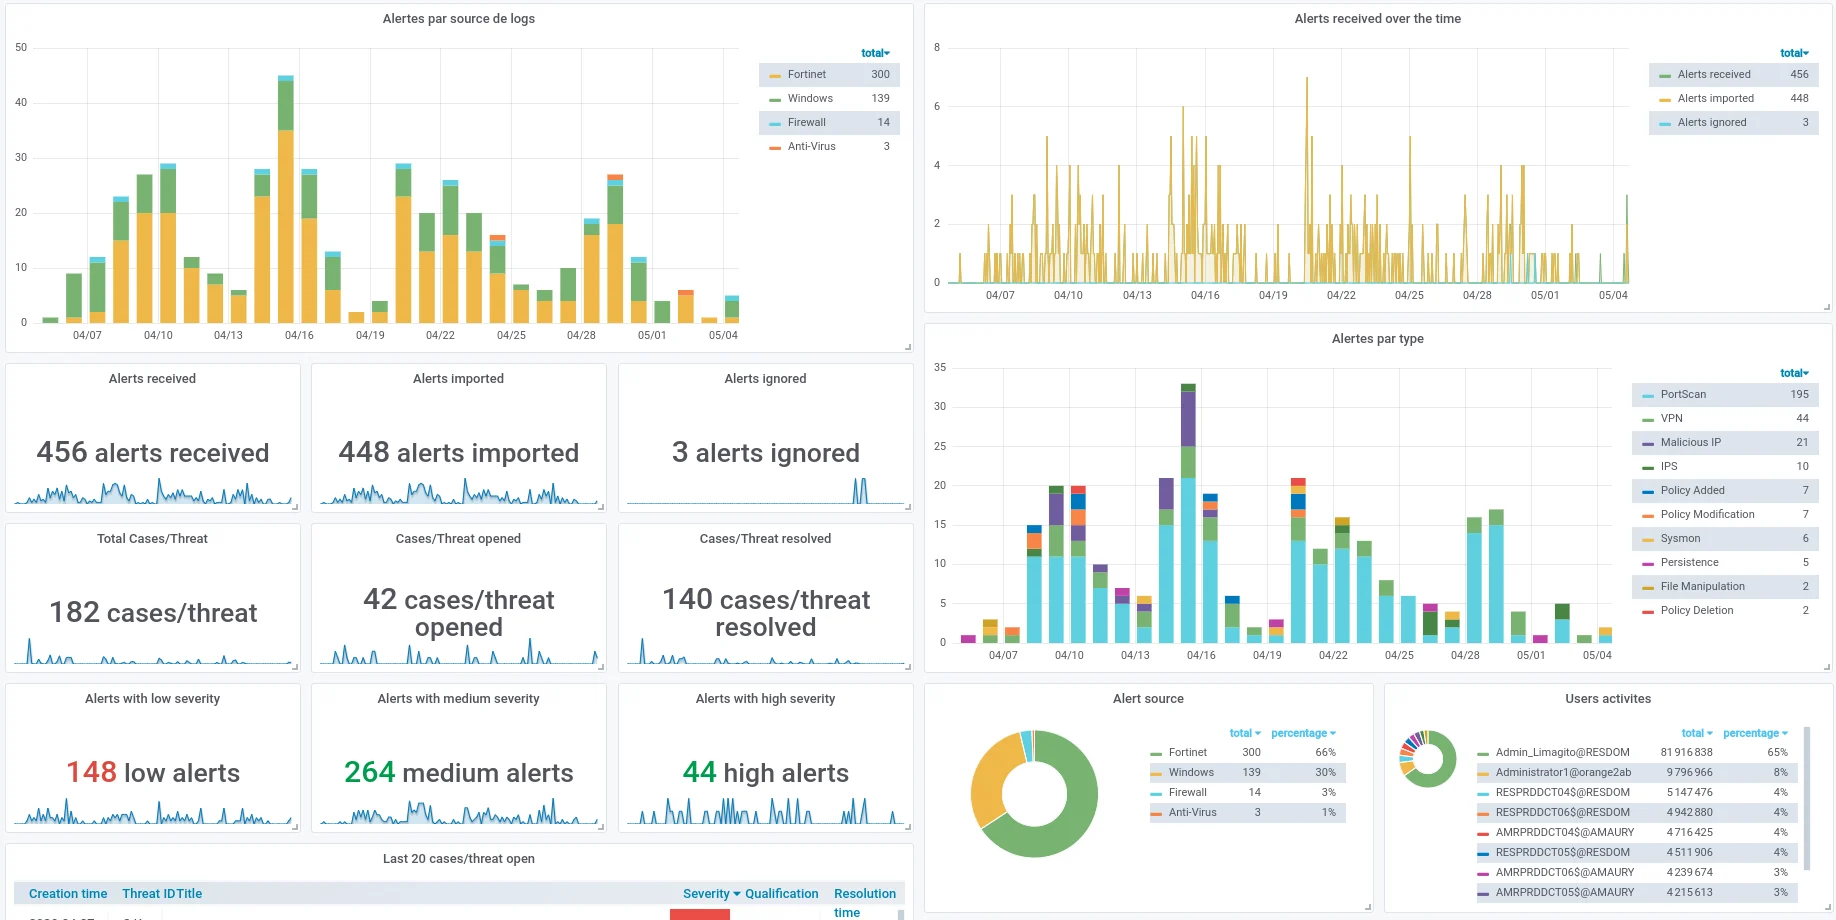
Reporting and Key Indicators
The graphical web interface enables the analysis and generation of dashboards based on indexed data.
This visualization engine allows you to:
Run targeted searches,
Promptly identify rare events,
Visualize trends,
Monitor management and development KPIs,
Define compliance metrics,
Build custom dashboards. Dashboards can incorporate multiple rankings, charts, trends, and more to address the specific needs of various stakeholders: analysts, security managers, executive decision-makers, and beyond.
Taking it further
They rely on Reveelium
What our clients say
« We hadn’t identified any products on the market that could protect us against advanced cyber threats. Until we discovered Reveelium. We have been using it for several years and it allows us to move from a reactive model to a preventive model. We haven’t had a single incident for several years with this technology… »
 A. Godde, CIO, Nutrition & Santé
The sovereign SIEM